Flock Gets Authority to Issue CVEs for Its Surveillance Products
Flock's New Role in the CVE Program
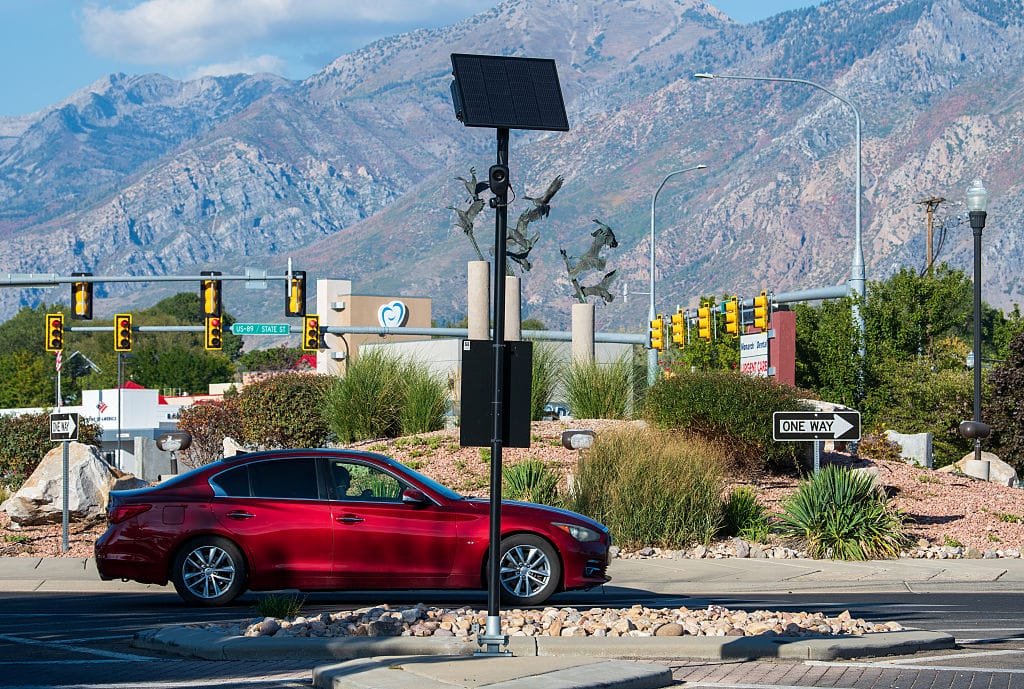
Flock has officially joined the Common Vulnerabilities and Exposures (CVE) Program as a Coordinating Node for Analysis (CNA). This new designation grants Flock the authority to assign unique identifiers to vulnerabilities discovered in its own surveillance cameras and license plate readers. This development marks a significant step for the company, enhancing its position within the cybersecurity landscape.
Historically, the CVE Program has been crucial in standardizing the identification of vulnerabilities across various technologies, facilitating better communication and response strategies among security professionals. By allowing Flock to issue CVEs for its products, the program acknowledges the growing importance of surveillance technology in public safety and law enforcement domains. However, this also raises questions about the trustworthiness of self-reporting by companies regarding their own vulnerabilities. Flock’s ability to evaluate and disclose issues in its products could lead to concerns about potential conflicts of interest and transparency.
As Flock gains increased responsibility, it also faces heightened scrutiny from both industry stakeholders and consumers. The implications of this authority could shift how vulnerabilities are perceived and addressed within the surveillance technology sector. Organizations relying on Flock's products may need to reassess their risk management strategies, considering the balance between innovation in surveillance capabilities and the security risks that may arise from vulnerabilities in these systems. This development could prompt broader discussions about accountability and the role of manufacturers in ensuring the cybersecurity of their products.
Sources: Cyberscoop, Flock Safety, Pasquale Pillitteri, and Nextgov/FCW
Edited by Daniel Vazdar, Editor. How DEFCROS News reports, sources and corrects.