FortiBleed Campaign Targets Over 400,000 Fortinet Devices, Poses Ransomware Risks
Active Threat Landscape
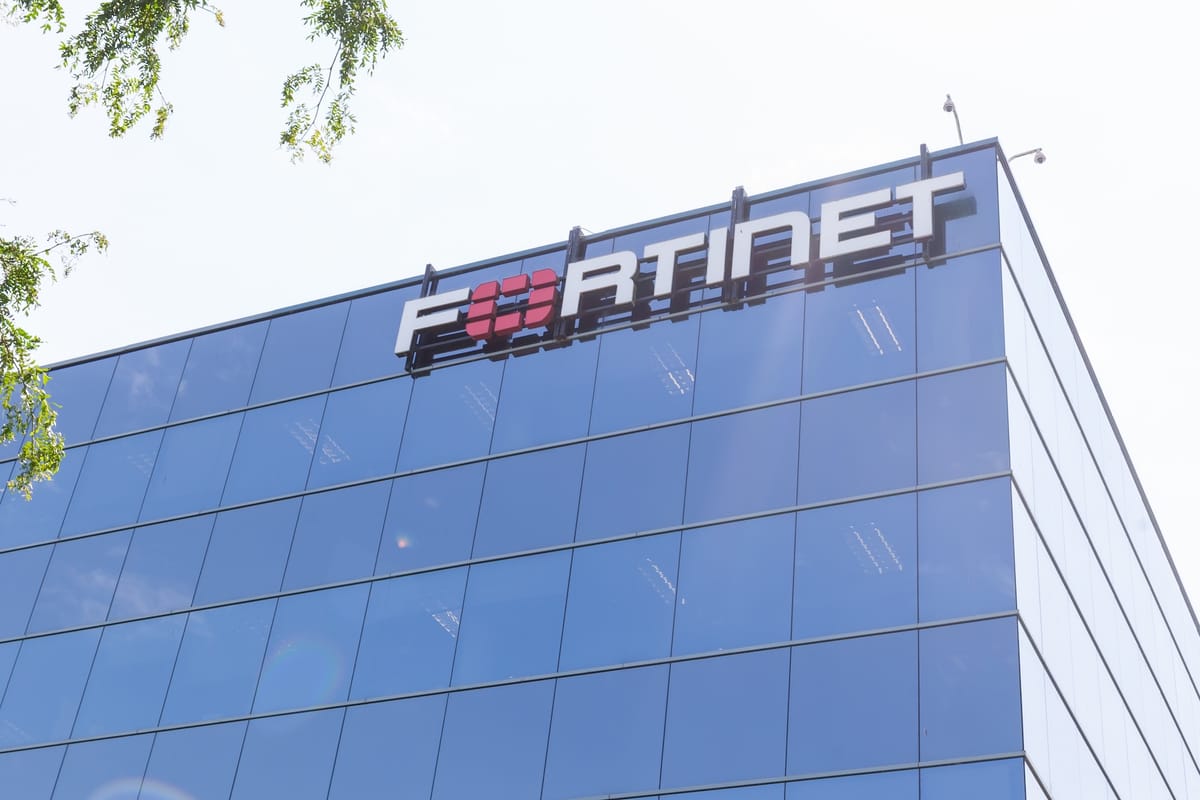
The FortiBleed campaign has emerged as a serious cybersecurity threat, actively targeting more than 400,000 Fortinet devices. This ongoing attack, highlighted by the FBI and Secret Service, is capable of locking users out of their systems and facilitating ransomware attacks.
As organizations increasingly rely on Fortinet's security appliances, the implications of this campaign are significant. The vulnerabilities exploited in these devices could undermine the integrity of critical infrastructure, making it essential for IT teams to address potential breaches swiftly. The ability of attackers to lock users out adds a layer of urgency to the situation, as organizations must prepare for both operational disruptions and the potential for extortion through ransomware.
Operational and Security Implications
The FortiBleed campaign not only highlights existing vulnerabilities but also underscores the importance of maintaining robust cybersecurity protocols. Organizations are urged to review their security measures and apply necessary patches to Fortinet devices to mitigate risks. Failure to act could result in significant operational challenges and financial losses due to ransomware demands.
This situation necessitates a reevaluation of incident response strategies across affected sectors. As more details unfold, the focus will likely shift to how organizations adapt to these cybersecurity threats and enhance their defenses against potential future attacks.
Sources: Cyberscoop, The Cyber Express, Industrial Cyber, SecurityWeek, and The Hacker News
Edited by Daniel Vazdar, Editor. How DEFCROS News reports, sources and corrects.